Company Spotlight · Sponsored
HL Hunt Pay Offers Three Ways to Take a Payment. The Difference Between Them Is Who Carries the PCI Burden.
Prior coverage of HL Hunt's AI payment processing product looked at its pricing, its dispute-handling agents, and its chat-based assistant. Less examined is the actual checkout mechanics: a hosted page, an embedded snippet, or a full custom build on the API — each shifting compliance responsibility differently.
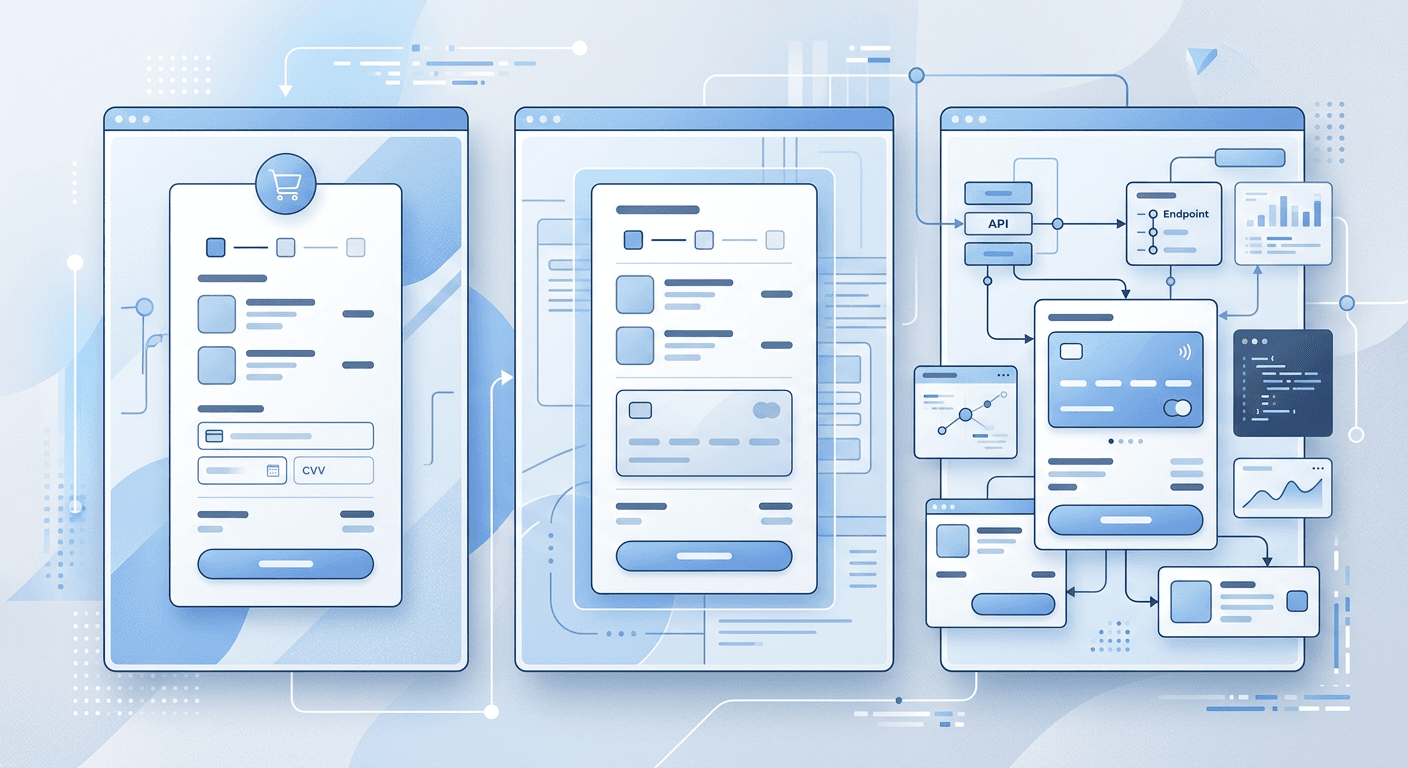
SPONSORED CONTENT — Earlier coverage of HL Hunt Pay, HL Hunt Financial's payment processing product, has looked at its self-authored pricing comparison against Stripe and Square, the AI agents it runs against disputes and failed payments, and the chat-based assistant that lets merchants send invoices in plain English. One part of the product page that has gotten less attention is more basic and arguably more consequential for a merchant actually evaluating the platform: the three distinct ways a business can implement checkout, and what each one means for who carries PCI compliance risk.
The first option is a hosted checkout page — a URL at checkout.hlhunt.org that HL Hunt controls entirely. A merchant sends a customer a link, the customer enters card details on HL Hunt's infrastructure, and the merchant never touches cardholder data at any point. This is the lowest-effort and lowest-liability option: no code, no website required, and the PCI compliance burden sits entirely with HL Hunt rather than the merchant, since the merchant's systems never process or store card numbers.
The second option, embedded checkout, drops a pre-built HL Hunt component directly into a merchant's own website or app with a single code snippet. The customer never leaves the merchant's page, which is better for conversion and brand consistency than redirecting to a hosted URL, but the payment fields themselves still run inside HL Hunt's PCI-compliant vault rather than the merchant's own servers — the product page's language is explicit that this preserves the "no compliance headaches" position of the hosted option while looking native to the merchant's site.
The third option is a fully custom build on HL Hunt's REST API and SDKs, with tokenized card fields and webhooks for every event — disputes, refunds, payouts. This is the option aimed at merchants who want full control over the checkout experience, including split payments and marketplace-style flows, but it also puts more of the implementation work and PCI scope on the merchant's own development team, since a custom build necessarily involves the merchant's code handling more of the payment flow directly, even with tokenization limiting what raw card data ever reaches it.
None of the three options is objectively better; they trade off against each other predictably, with less merchant effort and liability correlating with less control over the checkout experience. What is worth flagging is that the PCI DSS Level 1 certification HL Hunt cites, and the comparison table on the same page crediting itself with fewer account shutdowns and lower fees than Stripe and Square, are both self-reported by HL Hunt rather than independently verified by this publication. A merchant choosing among the three checkout paths should weigh that against its own compliance capacity and risk tolerance, not against HL Hunt's own characterization of how it stacks up against named competitors.